Grafana Loki
Overview
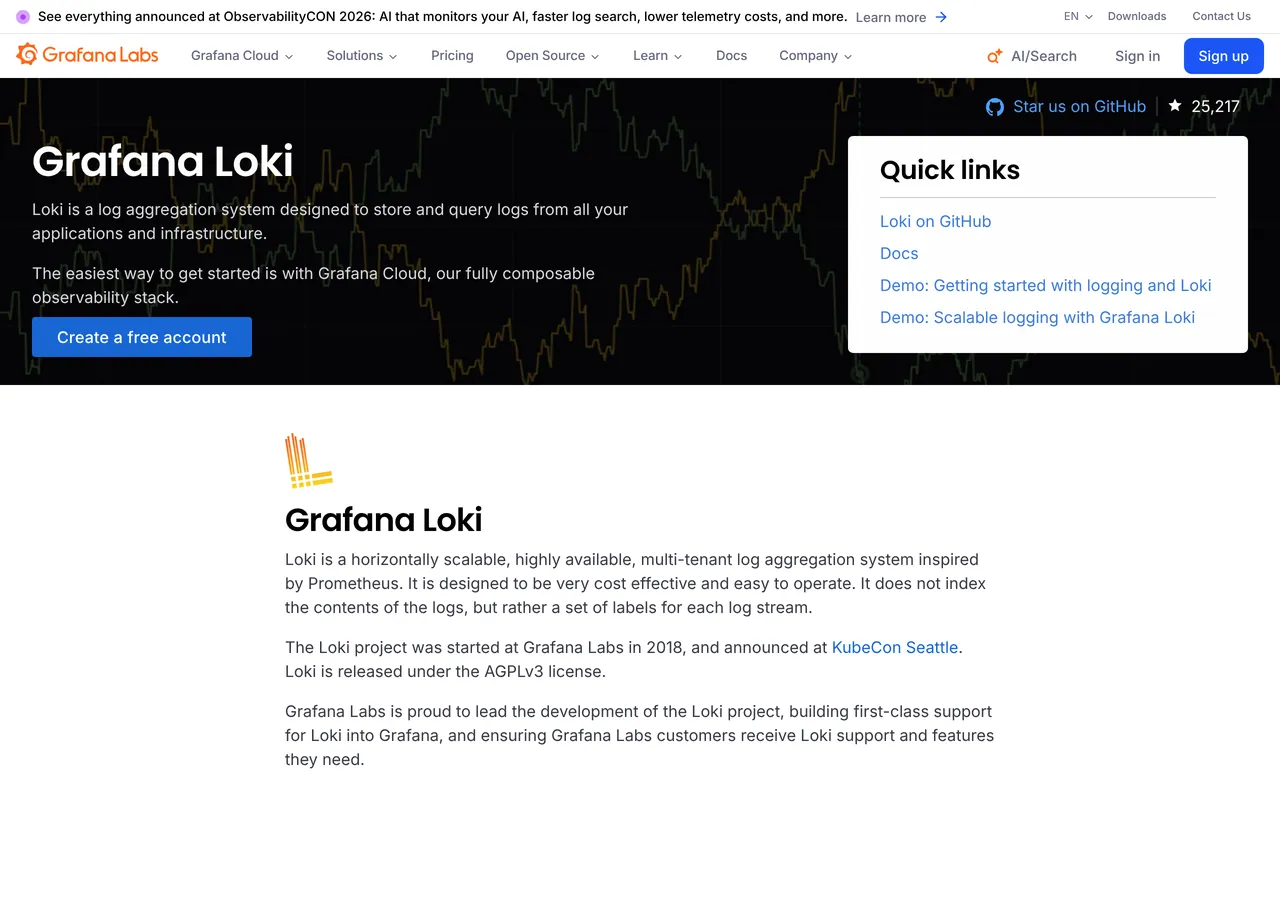
Grafana Loki is a horizontally scalable, highly available, multi-tenant log aggregation system inspired by Prometheus. Instead of indexing the full text of your logs, it indexes only a set of labels for each log stream, which makes it simpler to operate and cheaper to run. It is developed by Grafana Labs.
What it does well
Loki stores compressed logs and indexes only metadata, using the same labels you already use with Prometheus, so you can switch between metrics and logs easily. It is a particularly good fit for Kubernetes pod logs, whose labels are picked up automatically. A typical stack uses Grafana Alloy to collect logs, Loki to store and query them, and Grafana to explore them.
Why it’s in the collection
Loki brings log storage costs down dramatically by not indexing everything, and fits naturally next to Prometheus and Grafana. It is AGPL-licensed.
On GitHub
- Stars
- 0
- Forks
- 0
- Commits
- 0
- Repository
- grafana/loki
Languages
- Go 98.5%
- Jsonnet 0.7%
- Other 0.8%
Compared with
 SplunkCommercial platform for searching and analyzing machine data and logs.
 DatadogHosted monitoring and log management platform, priced by usage.
 ElasticNo. 053Search and analytics engine often used to store and search logs.
See every open-source alternative to Splunk and Datadog in the collection.